Don’t let automation make blind decisions.
Automation can only act on what it can see. Understand adversary behavior and intent early before a wrong decision turns a small threat into a big one.
Trusted worldwide

Designed to see
attacks at their earliest stages.
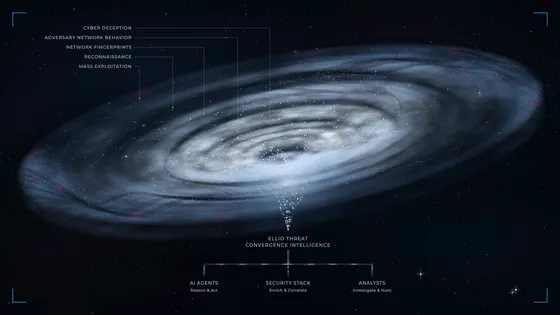
See the full picture of early-stage attack activity across threats, targets, tooling, infrastructure, and their relationships. Connect fresh evidence as it happens and act before threats escalate into costly incidents.
Adversary Network Intelligence
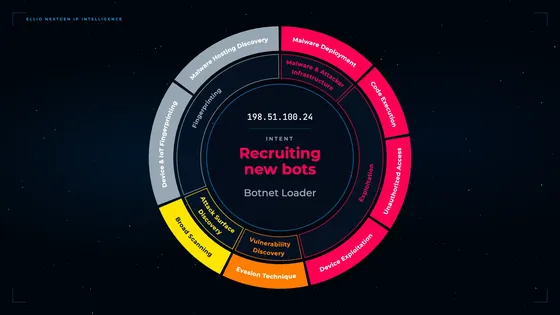
NextGen IP Intelligence tailored to agentic security.
Reconnaissance Threat Intelligence
See attack preparation before exloitation.
Mass Exploitation Intelligence
Track how exploitation activity happens before escalating.
Network Fingerprint Intelligence
See the threats behind fragmented infrastructure.
Direct observation.
First-party telemetry.
ELLIO operates its own distributed cyber deception network, providing a first-party vantage point into adversarial activity on the Internet - from reconnaissance and probing to exploitation and follow-on activity.
- High-fidelity signals
- Direct observations of live activity
- No third-party data noise
ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.

ELLIO Gets a Major Upgrade in Its Recon & Mass Exploitation Intelligence
Today, we’re releasing a major set of improvements to ELLIO Reconnaissance and Mass Exploitation Intelligence.

wp2shell in the Wild: From Patch to Mass Exploitation in Under 48 hours
The ELLIO Deception Network recorded more than 11,500 sessions across 700 sensors as traffic moved from probing to attempted database extraction, administrator creation, and a web-shell write. The first probe arrived the morning after WordPress published its fix.
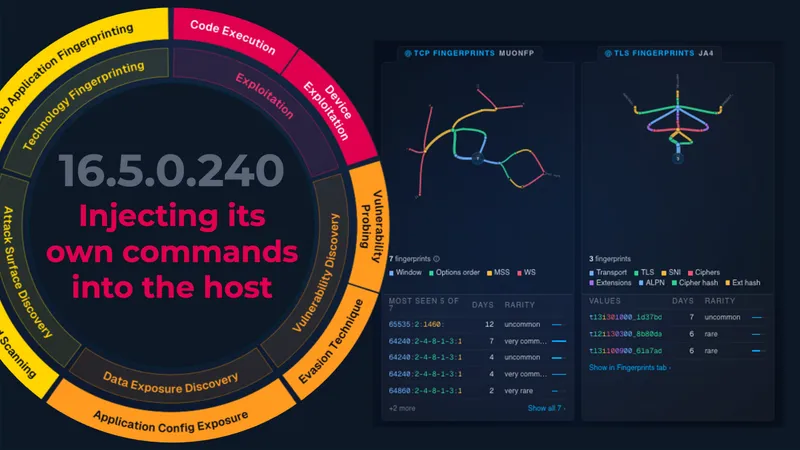
The Intelligence Value of Network Fingerprinting
Two connections come from different IPs. Are they related? Network fingerprints give analysts another way to compare traffic, investigate suspicious activity and make decisions when reputation data offers few answers. But be careful: a fingerprint is only as useful as the interpretation behind it.
Microsoft Security Naming Survival Guide
A quick guide to Microsoft security name changes, helping you make sense of current terms without getting lost in older names.

Why Microsoft Sentinel Feels Noisy: It’s Not Volume, It’s Recon Blindness
Alert fatigue in Microsoft Sentinel is not caused by alert volume alone. It is a context and correlation problem. Read how reconnaissance-aware threat intelligence helps separate internet scanning noise from active exploitation activity to improve signal quality and reduce false-positive incidents.