
Don’t let automation work with half the picture.
Add live reconnaissance, exploitation, infrastructure, and behavioral context to the security automation you already use, giving automated workflows the context to identify activity that warrants attention and trigger the right response.
Telemetry designed to catch
attacks at their earliest stages.
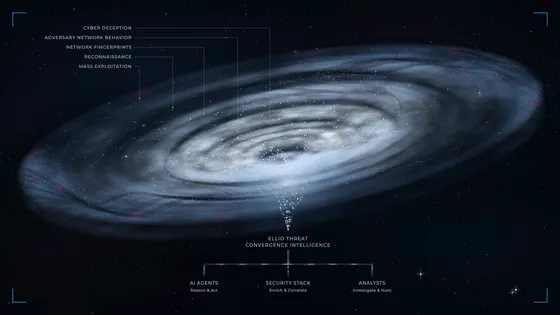
Get direct, first-party observations of early attack activity across targets, tooling, infrastructure, and their relationships from the global ELLIO Deception Network. Feed fresh signals into your SIEM, SOAR, and security AI to identify active targeting, connect attack progression, and trigger defense before it turns into costly incidents.
Reduce Unnecessary Security Escalations
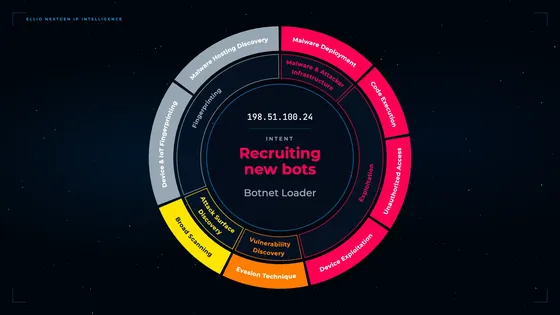
Distinguish routine scanning from targeted reconnaissance and exploitation using observed source behavior, giving automated workflows a stronger basis for escalation.
Detect Attacks While They Are Developing
Link reconnaissance and vulnerability probing to subsequent exploit activity, allowing automation to act on attack progression rather than isolated events.
Prioritize Vulnerabilities Under Active Exploitation
Link observed exploit attempts to CVEs and targeted assets, allowing remediation workflows to prioritize vulnerabilities under attack.
Prevent Repeat Attacks From Bypassing Automation
Keep automated defenses from treating every new attacker IP as a new threat, using ELLIO to connect related activity across changing infrastructure.
Avoid blind spots
in threat intelligence.
Extend threat intelligence with early-stage threat expertise to avoid incomplete context, incorrect dassessments, and unnecessary threat escalation.
Network Adversary Intelligence
NextGen IP Intelligence tailored to agentic security.
Reconnaissance Threat Intelligence
See attacks preparation before exploitation.
Mass Exploitation Intelligence
Track how exploitation activity happens before escalating.
Network Fingerprint Intelligence
See the threats behind fragmented infrastructure.

