
Add extra protection against active threats and live scanning.
Strengthen your firewall with live intelligence on IPs actively scanning, probing, and exploiting exposed systems. Block malicious traffic and unwanted reconnaissance at the edge, before it reaches your network.
INTEGRATES WITH MAJOR NGFW




Using ELLIO’s blocklist service, deception intelligence, and network fingerprints, we quickly deployed the relevant blocklists to our production firewalls and contained the attack before it could gain traction. The intelligence also allowed us to proactively verify and remediate the targeted infrastructure, adding an additional layer of defense.
Ken Webster
Sr. Incident Response Leader, · Imperva - Thales Company
Powered by NextGen IP Intelligence and live evidence.
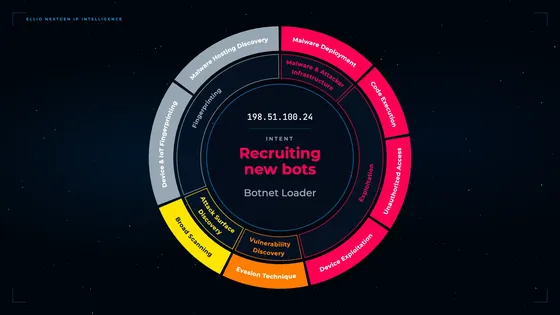
ELLIO combines first-party observations with behavioral, infrastructure, and relationship data to show what an IP is doing now - from scanning and probing to active exploitation. Use that live context to update IP rules and blocklists automatically, stop active threats at the edge, and avoid blocking legitimate traffic based on reputation alone.
Custom Blocklist Configuration
9 rules
Firewalls
5 targetsCustom Blocklist Configuration
9 rules Firewalls
5 targets
Compared to other security solutions, ELLIO doesn't require constant supervision and handles zero-day attacks better. Thus, we've partnered with ELLIO to bring their technology to the ntop user community.
Luca Deri
Founder · ntop
Stronger perimeter.
Less SOC noise.
Block active threats before they reach your network and keep routine Internet activity from becoming SOC alerts.

See how ELLIO works for you.
Start Free TrialHow is ELLIO different from traditional IP blocklists?
ELLIO provides dynamic IP intelligence based on real-time observations from its own cyber deception network. Instead of relying mainly on static reputation or known-bad lists, it uses observed reconnaissance, probing, exploitation, and infrastructure relationships to identify IPs involved in active attack activity.
Because the intelligence is based on current behavior, it can surface attack infrastructure before it appears on traditional blocklists. ELLIO is also fully configurable, so you can apply different rules and feeds to strengthen automated blocking while reducing unnecessary blocks of legitimate traffic.
Traditional blocklists tell you what an IP is known for. ELLIO adds evidence of what that IP is doing now.
How is ELLIO different from CrowdSec, Spamhaus, and other IP blocklist providers?
ELLIO continuously correlates observed activity and infrastructure relationships to identify IPs involved in active attack activity. High-frequency updates can then be fed into firewalls and other security controls for automated enforcement, helping teams respond to emerging threats before they become established in static reputation feeds.
Unlike traditional blacklist providers, ELLIO focuses on what an IP is doing now, not only what it is known for. That additional context helps security controls distinguish active attack infrastructure from legitimate or benign Internet activity, reducing unnecessary blocking while strengthening automated perimeter defense.
Does ELLIO integrate with existing firewalls?
Yes. ELLIO integrates with major firewall and network security platforms, including Palo Alto Networks, Check Point, Fortinet FortiGate, Cisco, Microsoft Azure, Sophos, F5, and ntopng. It also supports open-source platforms such as OPNsense, pfSense, and Linux-based firewalls, including deployments using Traefik.
Connect ELLIO to your existing security controls and configure the blocklists, allowlists, and rules that fit your environment. ELLIO keeps the intelligence feeds updated, so your firewalls can automatically apply current IP intelligence without manual list synchronization.
Can I configure ELLIO IP blocking according to my needs?
Yes. ELLIO IP Blocklists are fully configurable through ELLIO Blocklist Automation, giving security teams precise control over what is blocked and what must remain accessible across all managed firewalls. You can create custom blocklists per customer or environment, prioritize high-risk infrastructure tied to mass exploitation, and ensure trusted services - like SaaS platforms, partners, and approved scanners - are never disrupted. All policies are automatically enforced across your multi-vendor firewall environment, without manual overhead.
How does ELLIO affect false positives and SIEM noise?
ELLIO blocks only active malicious and high-risk IPs involved in active reconnaissance or mass exploitation, while ensuring critical business services, SaaS platforms, and essential bots always remain allowed.
Its fine-grained IP rules let you control exactly what gets blocked or allowed, preventing disruptions to core infrastructure. This approach drastically reduces false positives and unnecessary SIEM alerts, so security teams can focus on real threats instead of chasing noise.
How is ELLIO valuable for MSPs offering managed firewall services?
ELLIO extends managed firewall services with preemptive protection against reconnaissance and mass exploitation, going beyond what firewall vendors and static blocklists deliver. MSPs can automatically block attacker infrastructure before it turns into customer incidents, while ensuring critical business traffic is never disrupted.
Built as a multi-tenant platform, ELLIO allows MSPs to manage customizable blocklists per customer and enforce them consistently across multi-vendor firewall environments. This reduces operational overhead, lowers SIEM noise, and enables MSPs to deliver a scalable, intelligence-driven security service that clearly differentiates their offering.