Threat intelligence on mass exploitation & recon activity for SOC workflows.
Gain real-time intelligence and context on mass exploitation and reconnaissance activity as it happens. ELLIO enriches and correlates security data to help identify and prioritize relevant threats over benign activity - reducing risk, cost, and SOC workload.


Reduce SIEM noise from mass automated traffic
Improve signal-to-noise ratio by filtering high-volume scanning, reconnaissance, and bot-driven traffic in real time. Isolate active malicious activity from background internet noise as it happens, improving alert quality, reducing false positives, and helping SOC analysts focus on what actually matters.
Stop repeat attacks behind rotating IP infrastructure
Correlate distributed reconnaissance and mass exploitation activity across changing IP addresses to detect persistent attacker campaigns, not just individual sources. Block behavior patterns instead of chasing single IPs.
Clean SIEM signals through perimeter-level intelligence
Combine perimeter defense and signal reduction in a single layer. Filter low-value and redundant traffic at the perimeter to improve alert quality in SOC workflows. Keep critical services explicitly allowed while blocking active malicious traffic at the first security layer, before it escalates into a costly incident.
Go beyond noise reduction.
ELLIO Threat Intelligence is designed for SOC-wide operational use, from human-led investigations to automated response workflows.
Context for human investigation & incident response
Data enrichment & automation for SIEM, SOAR, TIP, and other tools
Ground-truth metadata for AI agents & AI-assisted detection and analysis
Power automation with actor-level intelligence.
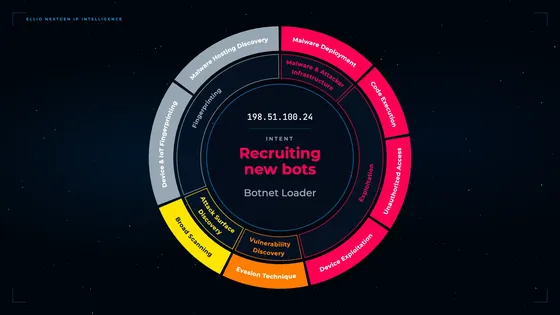
With ELLIO, you continuously enrich IP-based alerts linked to active mass exploitation and reconnaissance activity with the latest actionable context. Beyond basic IP classification, enriched intelligence includes:
Behavioral fingerprints
Identify scanning and exploitation tools even if the attacker rotates IPs.
Exploit history and CVEs
Map endpoints and payloads to real vulnerabilities.
Credentials and user agents
Track brute-force and login attempt patterns.
Historical activity timelines
See how targets, tactics, and tooling evolve over time.
MITRE ATT&CK mapping
Align with the MITRE ATT&CK framework to to correlate attack patterns.
Separate signal from background noise,
automatically.
ELLIO filters real reconnaissance and active mass exploitation from internet noise. It identifies scanners, AI scrapers, research crawlers, and botnets in real time, enabling your SIEM and SOAR to automatically deprioritize low-value alerts and focus on true risk.
Promiscuous mass internet scanners
AI/ML scraping tools
Opportunistic botnets
Benign research crawlers
Spray-and-pray campaigns
From global sensors to your security stack.
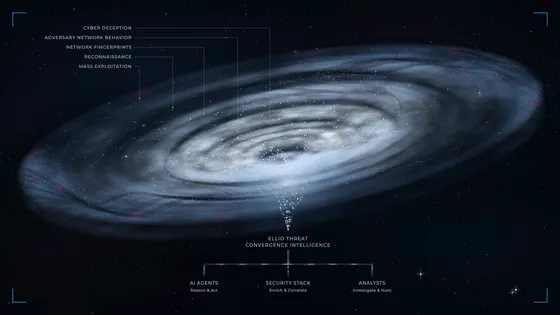
ELLIO Threat Intelligence flows from our global deception network through multiple channels, delivering actionable real-time insights directly into the security tools your team already uses.

"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.

ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.
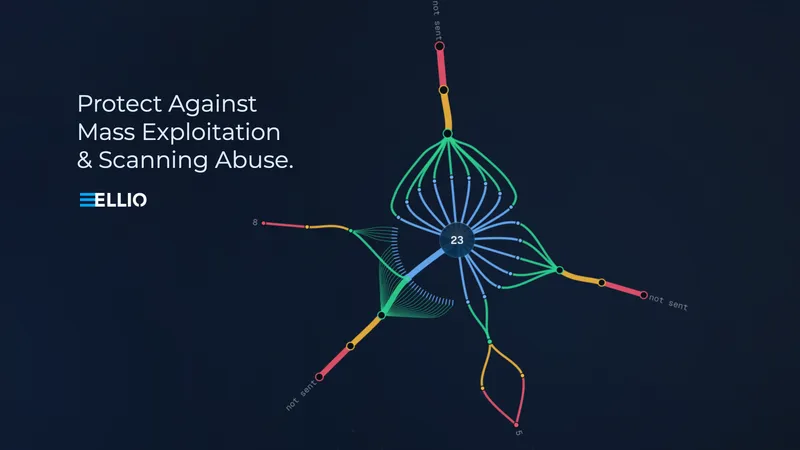
ELLIO Gets a Major Upgrade in Its Recon & Mass Exploitation Intelligence
Today, we’re releasing a major set of improvements to ELLIO Reconnaissance and Mass Exploitation Intelligence.
