Intelligence Capabilities
NextGen IP Intelligence tailored to autonomous security
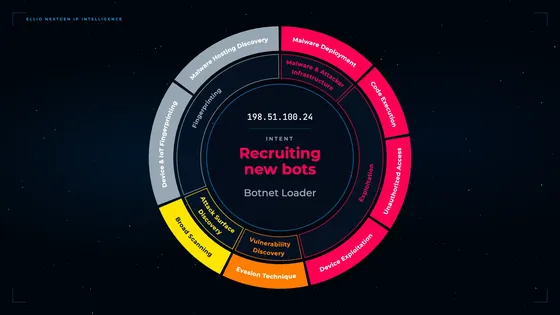
See attack preparation before exploitation
Track how exploitation activity happens before escalating
See the threats behind fragmented infrastructure
Direct observation. First-party telemetry.
Explore IP-to-hostname relationships
Intelligence delivery
Connect AI agents to ELLIO Intelligence
Put ELLIO Intelligence into your security stack
Stream or query ELLIO Intelligence
Get ELLIO threat data at scale
Block active attacks and live scanning at the edge
By Use Case
Investigate and respond faster
Patch what attackers target now
Reduce your exposure to attackers
Protection against active threats and scanners
Custom Blocking & Allowlisting Automation
By Teams
Speed up triage and response time.
Extend network defenses with visibility into live attacker infrastructure
Increase analyst capacity. Reduce unnecessary investigations.
Automate IP Blocking. Reduce routine work.
By Popular Ecosystem
Gain Visibility and Prioritize External Threat Exposure
Improve signal quality across all Sentinel workflows
Feed MISP with ELLIO’s non-spoofable attacker infrastructure intel
Extend FortiGate's Protection with ELLIO Threat Intelligence
View all supported ecosystems
Resources
Latest threat intelligence news and research
Technical docs and API reference
Get your MuonFP, JA4, and JA3 fingerprints
Key terms and concepts in threat intelligence
Open Source
Check what malicious, scanning or exploitation activity an IP is involved in
Access open CTI datasets to support academic research
Company
Who we are and what drives us
Our latest findings and product updates
Where we connect, share, and participate
Company news & anouncements
Contact us
Talk with ELLIO experts
Complete the form to get a quote
Send us a message via online form
Direct observations from live reconnaissance and exploitation reality.
See the full picture of early-stage attack activity across threats, targets, tooling, infrastructure, and their relationships. Connect fresh evidence as it emerges, and act before threats escalate into costly incidents.
ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.
Check an IP now. See what it’s scanning or exploiting.
Open the ELLIO IP Atlas to uncover what an IP is probing, scanning, or exploiting, what it is interacting with, and how its activity connects to related IPs, infrastructure, and targets.
We read reconnaissance as intelligence, not noise.
The earlier a threat is understood, the less it costs to contain. We built ELLIO around that conviction: look upstream, read the signals in reconnaissance, and understand where adversary attention is moving before activity becomes a campaign.
Tag: OpenSourceCybersecurity
At Black Hat 2025, ELLIO is launching a new open-source tool: the TCP Fingerprint Firewall. This Recon Shield, built on high-performance eBPF technology, uses advanced MuonFP-based fingerprints to detect and block malicious scanners in real time.