
Put ELLIO Threat Intelligence where your security teams work.
Enrich your existing security workflows with first-party intelligence from live reconnaissance and exploitation activity. Add current behavior, infrastructure relationships, and mass exploitation context to every IP. Cut through data noise, surface threats earlier, and reduce unnecessary processing,
ELLIO for Microsoft Sentinel
Connect the ELLIO CTI Feed via TAXII 2.1 to improve detection quality, automation workflows, and reduce noisy alerts. See when login attempts originate from IPs linked to active reconnaissance or exploitation activity.
ELLIO for Google Security Operations
Connect ELLIO CTI via API to bring dynamic observations from live reconnaissance, targeting, and exploitation activity into SIEM detection and investigation. Enrich findings, trigger SOAR response, and give Gemini richer threat context for more precise recommendations.
ELLIO for MISP
Correlate ELLIO observations with existing threat intelligence to strengthen analysis and sharing. Connect ELLIO CTI to enrich MISP events with dynamic intelligence on live reconnaissance, targeting, and exploitation activity.
See Who Is Scanning and Targeting Your Infrastructure
Detect IPs that are actively scanning, probing, targeting, or exploiting internet-facing systems, giving security controls visibility into attack activity that conventional IOC feeds may not capture.
Separate Threat Activity from Indicator Noise
Distinguish an IP simply appearing in telemetry from an IP actively involved in reconnaissance or exploitation, so detections and triage reflect what the infrastructure is doing now, not just what it was associated with previously.
Block Based on Active Attack Behavior
Use current observations of scanning, targeting, and exploitation as inputs to automated controls, enabling response decisions based on observed attacker behavior rather than static reputation or IOC matches alone.
Give AI Context Beyond Its Own Telemetry
Add ELLIO's external observations of attacker activity and targeted infrastructure to AI-powered security workflows, helping integrated AI interpret events with threat context that is not present in the organization's own telemetry.
Trigger the right response
before an attack escalates.
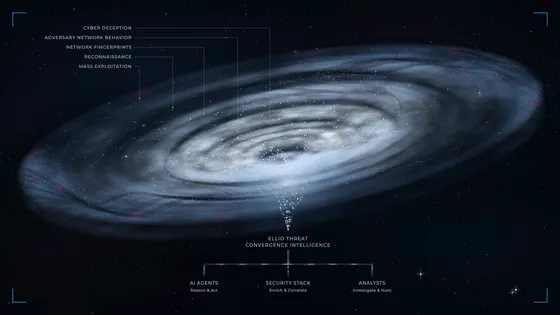
See the full picture of early-stage attack activity across threats, targets, tooling, infrastructure, and their relationships. Connect fresh evidence as it happens and act before threats escalate into costly incidents.
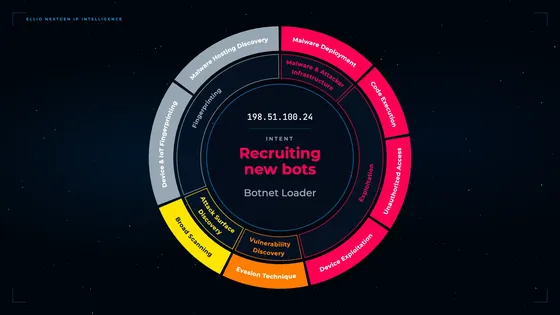
Adversary Network Intelligence
NextGen IP Intelligence tailored to AI-driven threat landscape.
Reconnaissance Threat Intelligence
See attack preparation before exploitation. Select noise from real threats.
Mass Exploitation Intelligence
Know what's exploited now. Track how exploitation activity happens before escalation.
Network Fingerprint Intelligence
See the threats behind fragmented infrastructure.
Don’t let blind spots drive security decisions.
Enrich IPs, alerts, and incidents with early-stage attacker behavior and infrastructure context that may not yet be present in internal telemetry. Enable AI produce better recommendations, prioritize emerging threats, investigate with richer context, and trigger the right response before an attack escalates.
- Direct observations of live scanning & exploitation activity
- High-fidelity signals
- Independent first-party intelligence