
Direct observation.
First-party telemetry.
ELLIO operates its own distributed cyber deception network, providing a first-party vantage point into adversarial activity on the Internet - from reconnaissance and probing to exploitation and follow-on activity.
During a credential-stuffing attack against one of our identity servers, ELLIO provided detailed intelligence from its deception network that helped us understand not only where the attack originated, but also its methods and intent. By showing us how the same threat actor had previously operated across the Internet, including the specific CVEs and tactics involved, ELLIO gave us the context needed to respond with confidence.
Ken Webster
Sr. Incident Response Leader · Thales Group
Don’t let blind spots drive your decisions.
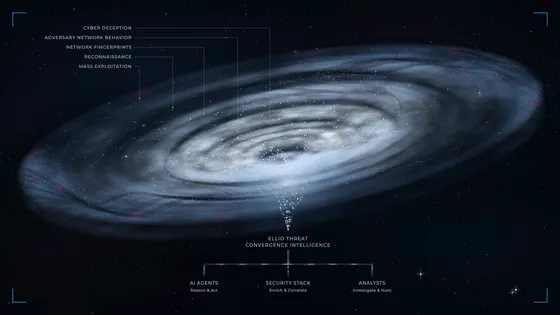
See the full picture of early-stage attack activity across threats, targets, tooling, infrastructure, and their relationships. Connect fresh evidence as it happens and act before threats escalate into costly incidents.
Adversary Network Intelligence
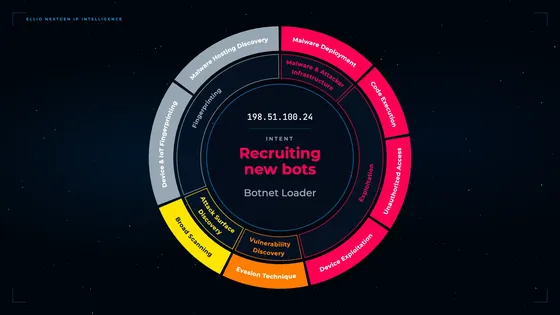
NextGen IP Intelligence tailored to agentic security.
Reconnaissance Threat Intelligence
See attack preparation before exploitation.
Mass Exploitation Intelligence
Track how exploitation activity happens before escalating.
Network Fingerprint Intelligence
See the threats behind fragmented infrastructure.
Don’t wait for attackers to reach you. See them coming.
Reconnaissance reveals where attackers are looking. Mass exploitation reveals where they are striking. ELLIO turns these live signals into early warning, helping security systems identify emerging threats, understand attacker behavior, and disrupt attacks before they reach your infrastructure.
- High-fidelity signals
- Direct observations of live activity
- No third-party data noise
Don’t wait for attackers to reach you. See them coming.
Reconnaissance reveals where attackers are looking. Mass exploitation reveals where they are striking. ELLIO turns these live signals into early warning, helping security systems identify emerging threats, understand attacker behavior, and disrupt attacks before they reach your infrastructure.
- High-fidelity signals
- Direct observations of live activity
- No third-party data noise
Node2Shell: remote code execution on stock Node.js builds (CVE-2026-111497)
A checker calling itself node2shell-check is already mapping which hosts decompress Brotli. CVE-2026-111497 turns a malformed Brotli body into a shell on an official, unmodified Node.js build, which ELLIO reproduced on x86-64 against four targets.

PHP2Shell: attacks before the patch, and automation by nightfall
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including what the attack tooling actually carried.
"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.