Emerging: First exploitation of Node2Shell (Broccoli2Shell a.k.a. HTTP2Shell) RCE observed in the wild. Read here.

Pricing

Threat Intelligence

Intelligence Package

Standard

Enrich & Automate via API

EUR36,000USD42,200GBP31,600 a year

Excluding VAT

  • ELLIO threat intelligence databaseย - 1M+ IPs a month involved in reconnaissance and mass exploitation
  • 5B+ threat and behavioural data points, covering reconnaissance, exploitation activity and CVEs
  • Real-time IP and network profilesย - up-to-date threat intelligence and network context for observed IPs
  • IP behavioural profiles and security tags, mapped to MITRE ATT&CK
  • Network Watchย - IP, IP range and ASN monitoring
  • Advanced network fingerprintingย - in-depth analysis of IP-associated network fingerprints
  • IP Activity Forecastย - up to 14 days ahead
  • IP activity historyย - 45 days
  • IP Blocking Packageย - 15-minute
  • Advanced multi-parameter search for researchers
  • 10 users

Intelligence Package

Advanced

Automate & Integrate at Scale

EUR48,000USD56,300GBP42,100 a year

Excluding VAT

Everything in Standard, plus:

  • Full integration access
  • MCP serverย - support for agentic workflows
  • Agent Automation Flowsย - ready-made workflows from triage to blocking
  • ELLIO KEVย - intelligence on actively exploited vulnerabilities
  • IP Intent Engine
  • rDNS Intelligence
  • IP Activity Forecastย - up to 30 days ahead
  • IP activity historyย - 60 days
  • 25 users

Intelligence Package

Custom

Tailored to Your Organisation

from EUR76,000USD89,000GBP66,600 a year

Excluding VAT

Everything in Advanced, plus:

  • New integrations on request
  • Historical access to all datasets
  • IP activity historyย - 90 days
  • IP Blocking Packageย - 5-minute
  • Unlimited users

Every package includes

  • Business-service check
  • IP reports
  • Single sign-on (SAML)

Canโ€™t find the right package? Get in touch and tell us about your use case and specific requirements. Weโ€™ll help you find the right solution.

Full comparison

Full comparison
Threat Intelligence StandardAdvancedCustom
Every package
The deception network ELLIO operates. We adapt it as attacks emerge and ahead of them, so everything you see comes from first-hand observation. Included Included Included
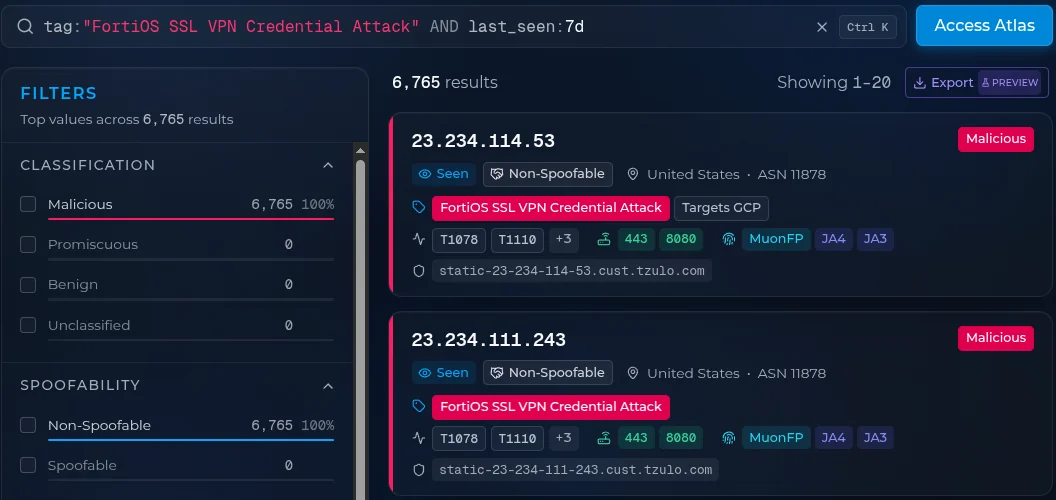
A web search in the ELLIO platform for IPs that attacked FortiOS SSL VPN logins in the last 7 days: 6,765 results. Web searches and IP profiles Search everything ELLIO observes with ELQ: find IPs by tag, CVE, ASN, fingerprint, HTTP path, user agent and more, then open any resultโ€™s IP profile. Unlimited Unlimited Unlimited
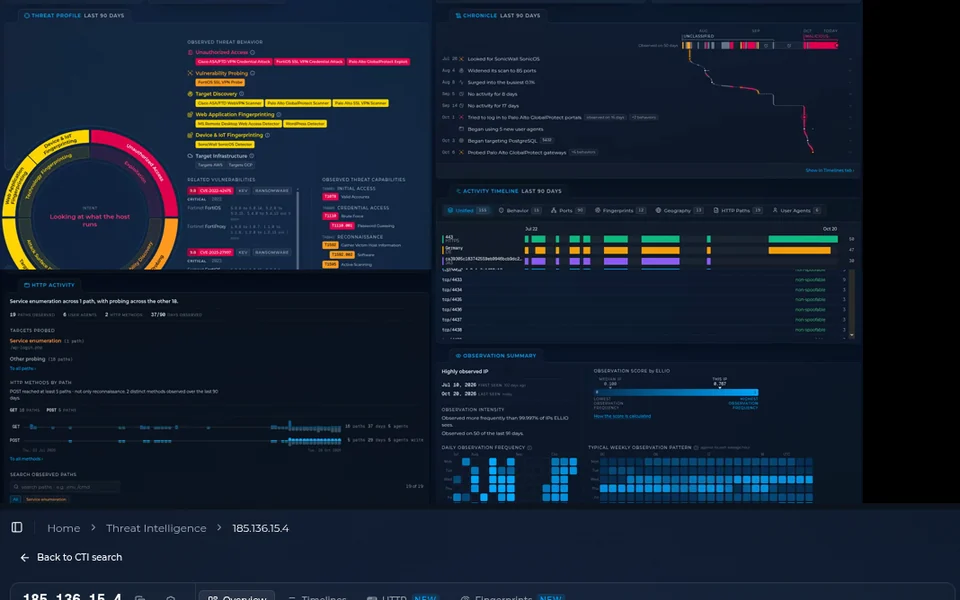
A scroll through one complete IP profile in the ELLIO web platform: activity and forecast, threat profile, network fingerprints, Chronicle, activity timeline, geographic footprint, HTTP and port activity, and the observation summary. Complete IP profiles Everything ELLIO has observed about an IP, on one page. Verdict: malicious, promiscuous, benign or unknownBehaviour profile and tagsFirst seen, last seen and how oftenWho it is, when known: scanner, botnet or research projectPorts targeted, with new ones flaggedHTTP paths, user agents and payload snippetsSSH usernames and passwords triedNetwork fingerprints: MuonFP, JA3 and JA4Network, hosting and the countries it targetedReverse DNS nameActivity timeline and Chronicle Included Included Included
Threat profile and observation summary for one IP: its intent, observed behaviour, and how often and when ELLIO sees it. Behaviour profiles What an IP has been doing, by category, and what it targets. Behaviour by categoryCVEs with CVSSKEV and ransomware flagsMITRE ATT&CK techniquesObservation summary Included Included Included
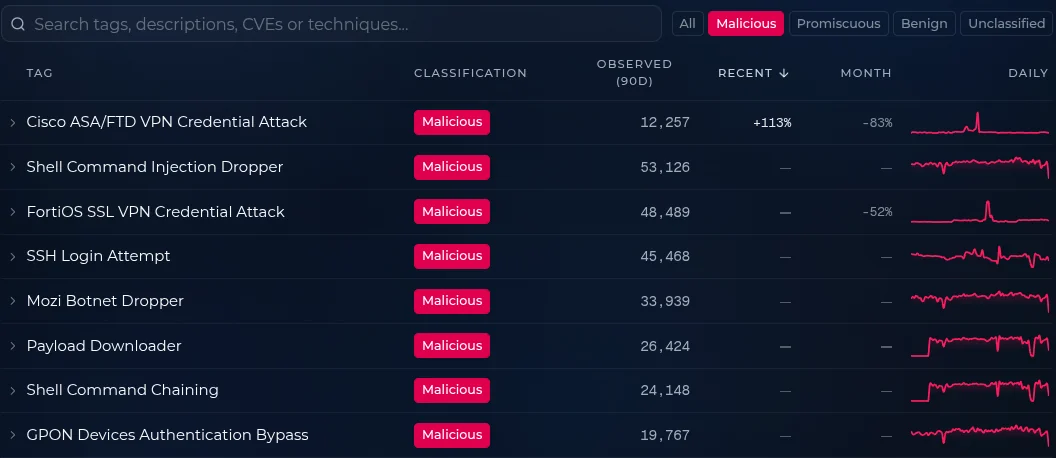
The ELLIO tag catalogue filtered to malicious tags, with IPs observed over 90 days and a daily trend for each tag. Behaviour tags Hundreds of tags name the tool, the exploit, the CVE and the targeted cloud, and new exploits are tagged as they appear. For each tag: the IPs seen, a daily trend and its MITRE ATT&CK mapping. Included Included Included
Whether an IP belongs to a known business service, such as a cloud provider, CDN, crawler or Microsoft 365, before you block it. Included Included Included
Exporting an IP report in the ELLIO platform as PNG, JPEG, SVG or PDF, then two pages of the branded six-page Unified Activity Timeline it produced. IP reports Export an IPโ€™s activity timeline as PNG, JPEG, PDF or SVG, for tickets, briefings and reports. Included Included Included
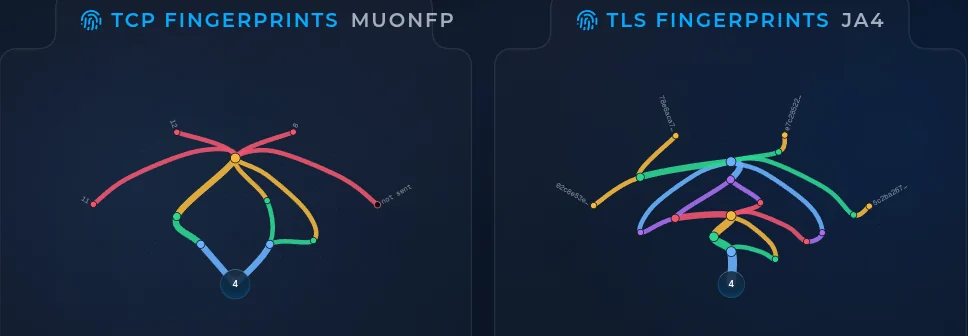
TCP (MuonFP) and TLS (JA4) fingerprint graphs for one IP, four fingerprints each. Advanced network fingerprinting In-depth analysis of the network fingerprints an IP presents: TCP (MuonFP) and TLS (JA3 and JA4). Included Included Included
Monitor the IPs, ranges and ASNs you choose, and see when they show up in ELLIOโ€™s data. Included Included Included
The complete Threat Intelligence API, for SIEM, SOAR, scripts and pipelines. Included Included Included
Users, history and outlook
Users 10 25 Unlimited
How far back you can look at an IPโ€™s activity, in IP profiles, web searches and the API. 45 days 60 days 90 days
IP Activity Forecast for one IP: a 79% chance of malicious activity within 7 days, rising to 94% within 30 days. IP Activity Forecast The likelihood that an IP shows malicious activity in the days ahead, from ELLIOโ€™s own prediction models. Up to 14 days Up to 30 days Up to 30 days
Automation
Connecting AI clients to the ELLIO MCP server: setup for Claude Code, Codex, Cursor, VS Code, Claude.ai and Claude Desktop, and ChatGPT. MCP server Connects your agents and AI clients to ELLIO for agentic workflows. While they work on a task, they can triage an IP, search ELLIO data, look up tags and act on your blocklists, with the access you grant. Works with ChatGPTClaudeClaude CodeCodexCursorVS CodeAny MCP client Not included Included Included
Your own agents, connected through the MCP server, follow ready-made flows: investigate an IP or triage a list of indicators, then add an IP to your blocklists, extend it or let it expire, with the access you grant. Not included Included Included
The vulnerabilities ELLIOโ€™s sensors see exploited right now: how many IPs exploit each one, the trend, and CISA KEV flags. For deciding what to patch first. Not included Included Included
What an IP appears to be trying to achieve, stated only as strongly as the evidence allows: what it did, what it looked for, or which services it touched. Not included Included Included
Integrations and datasets
Feeds and connectors that bring ELLIO data into your SIEM, SOAR and threat intelligence platforms. Not included All AllNew ones on request
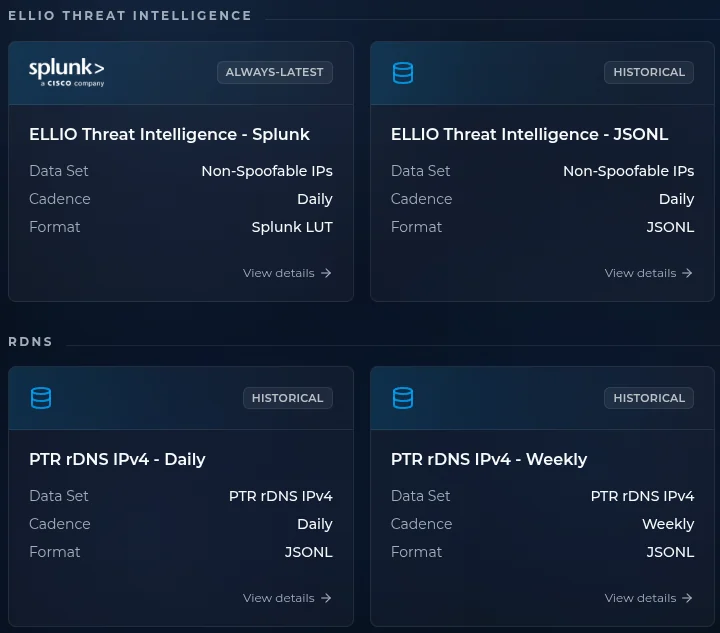
ELLIO bulk data: the Threat Intelligence dataset as daily JSONL, and PTR rDNS IPv4 as daily and weekly JSONL, each with history. Datasets ELLIO data delivered as files, for your own systems. Historical access adds every past file, not only the latest. Datasets Threat intelligence: every IP ELLIO observes, with every field, as daily filesrDNS: IPv4 PTR records, as daily and weekly files Not included All All + historical access
IP Blocking
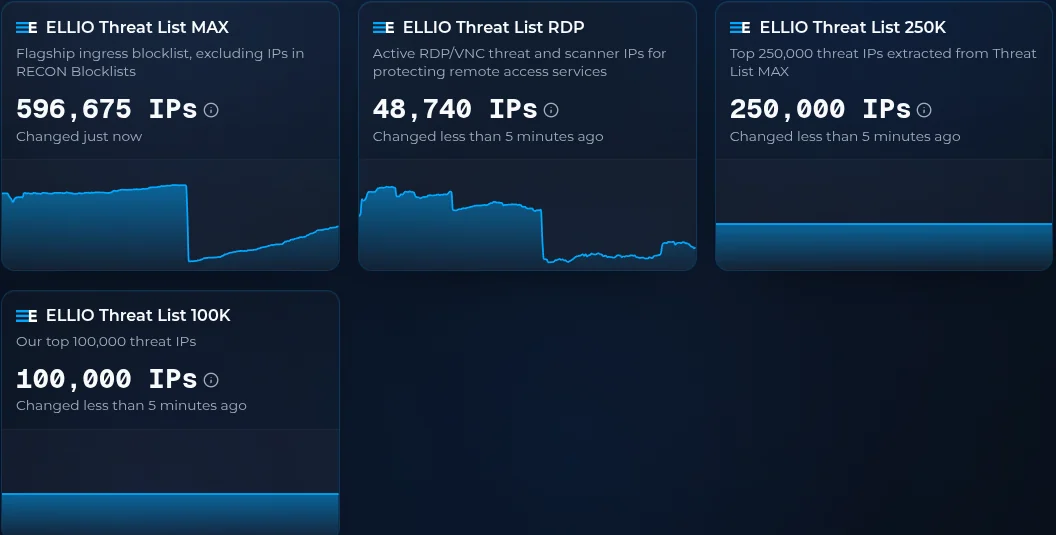
An IP Blocking Package included in the price: ELLIO lists on your firewalls, rebuilt automatically with the latest attacking IPs. Included Included Included
How often ELLIO rebuilds your lists with the latest attacking IPs. Every 15 minutes Every 15 minutes Every 5 minutes
End devices licensed to use your lists, such as firewalls, WAFs or routers. Each physical or virtual device counts, so an HA pair counts as two. 10 10 10+
Licence
For your organisationโ€™s own security work. Included Included Included
Managed service (MSSP) licence Not included Not included Not included
Price
Annual price Excluding VAT EUR36,000USD42,200GBP31,600 EUR48,000USD56,300GBP42,100 from EUR76,000USD89,000GBP66,600

Get my pricing quote ยท

from a year, excluding VAT

Company

Billing

Country *

Contact

Licence start date *
A bit about your team *

We will send the quote to your email address. By submitting this form, you accept our Privacy Policy.